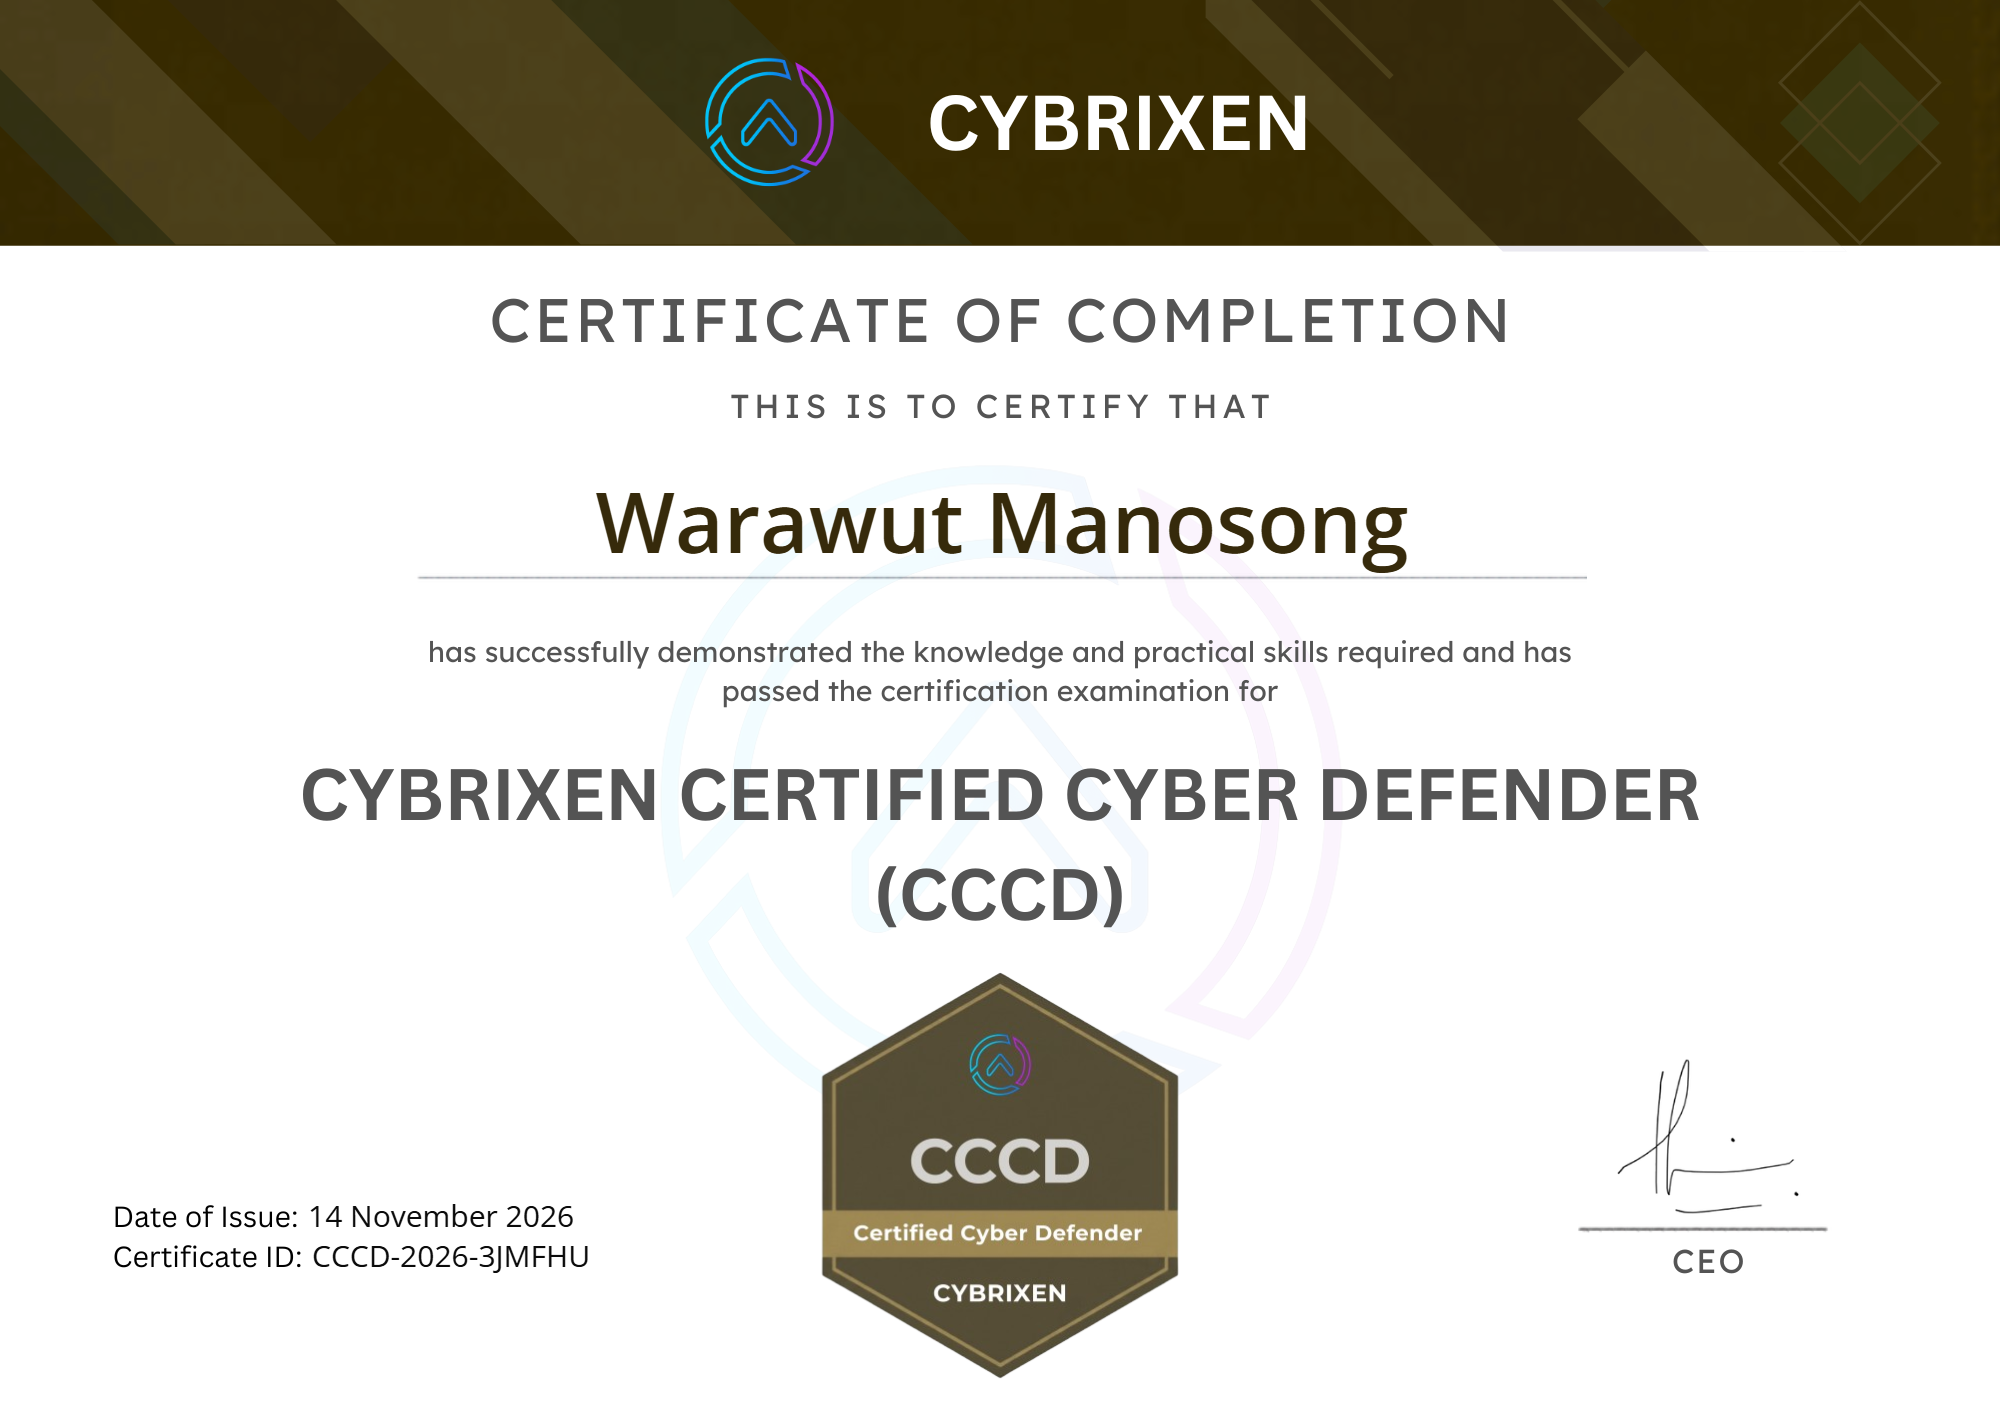
CCCD Exam Review: A 3D Shift as a Cyber Defender
Hello everyone, Chicken0248 here again with the CYBRIXEN Certified Cyber Defender (CCCD), my second blue team certification from CYBRIXEN after CCSA. To be completely honest, I got this exam for free when they first announced it on LinkedIn, because I hold CompTIA Security+. I never really appreciated having Security+ until I could use it to ask for free things 😄
I first heard about this platform from my friend Michał Sołtysik, who also told me to take the certification. (Let me tell you, he has been watching their site and LinkedIn page ever since he heard about them, waiting for certifications with cool names to finally drop.)
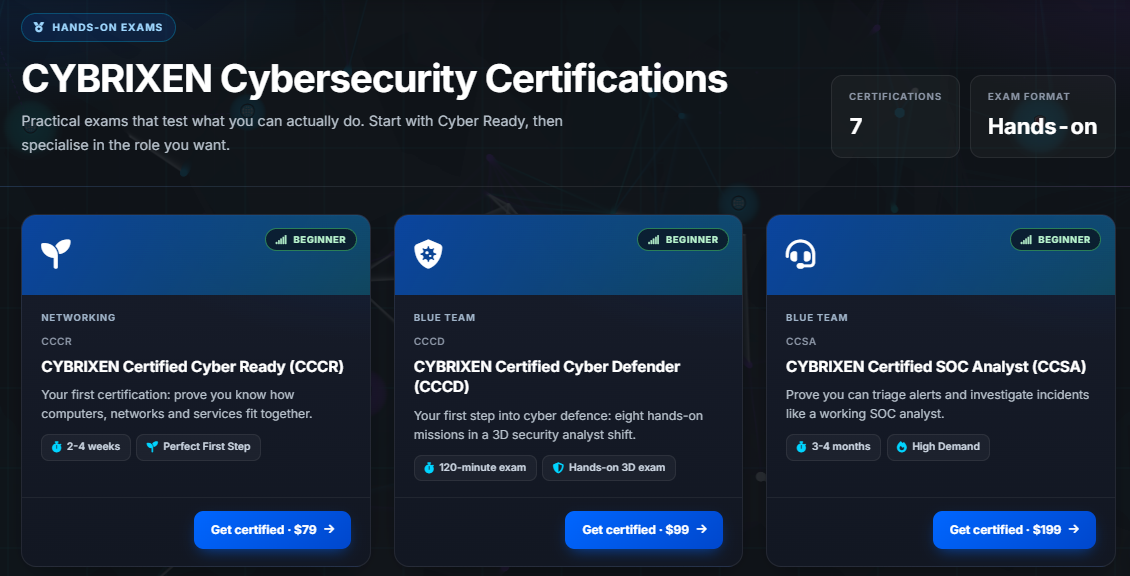
Let me bring up the cost and my feelings about this certification before we jump into the exam. CCCD costs 99 USD, way cheaper than their first blue team certification, CCSA. That makes me feel CYBRIXEN markets it as more entry level than CCSA, even though both are labelled Beginner.
You might also notice something about CCCD in the image above: what the hell is a "3D security analyst shift", and what is a "hands-on 3D exam"? That is what makes this exam unique in the entire cybersecurity industry, so let's find out in the next section!
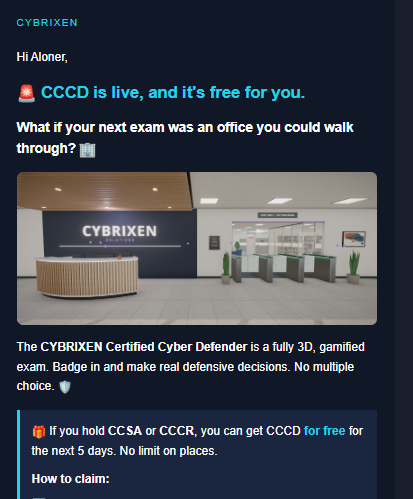
I have to admit I only noticed this email from CYBRIXEN while writing this review, because it had landed in my Promotions tab. It explains what is special about their new certification: a fully 3D, gamified exam. From the image in it, it looks like we are a security analyst who has to walk through each area of an office to solve specific security problems.
That sounds pretty unique compared with other certifications, right? Let's continue.
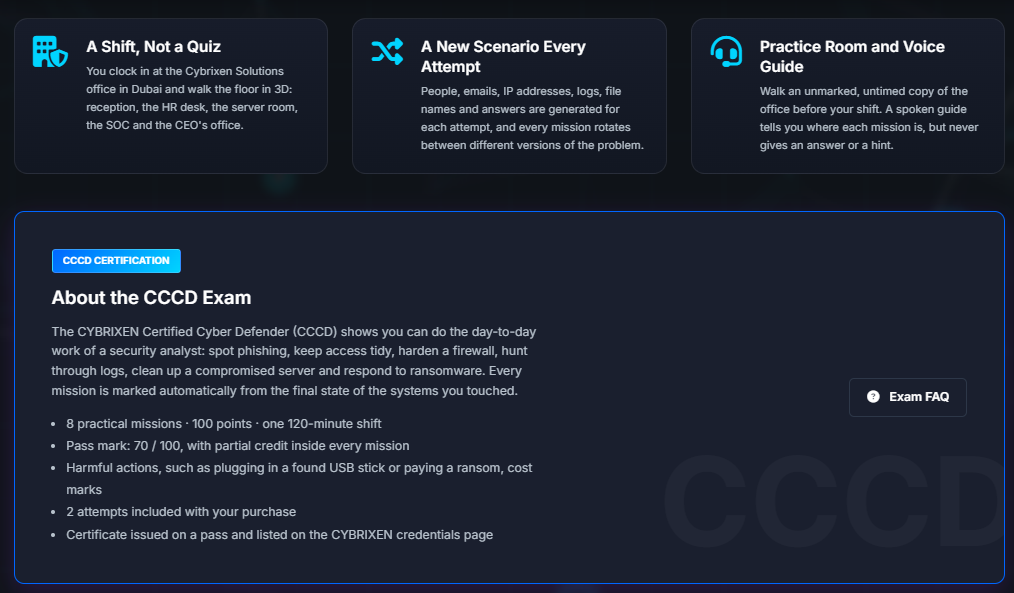
The CCCD page itself tells us that in that building we have to complete 8 missions within 120 minutes, scored out of 100, and 70 is the pass mark. These 8 missions are:
- Phishing triage
- Access review
- Clean-desk walk
- Firewall hardening
- SIEM investigation
- Endpoint forensics
- Ransomware response
And lastly, executive phishing. Given 2 hours to wander around the office, I would say it's pretty fair if you know what you are doing.
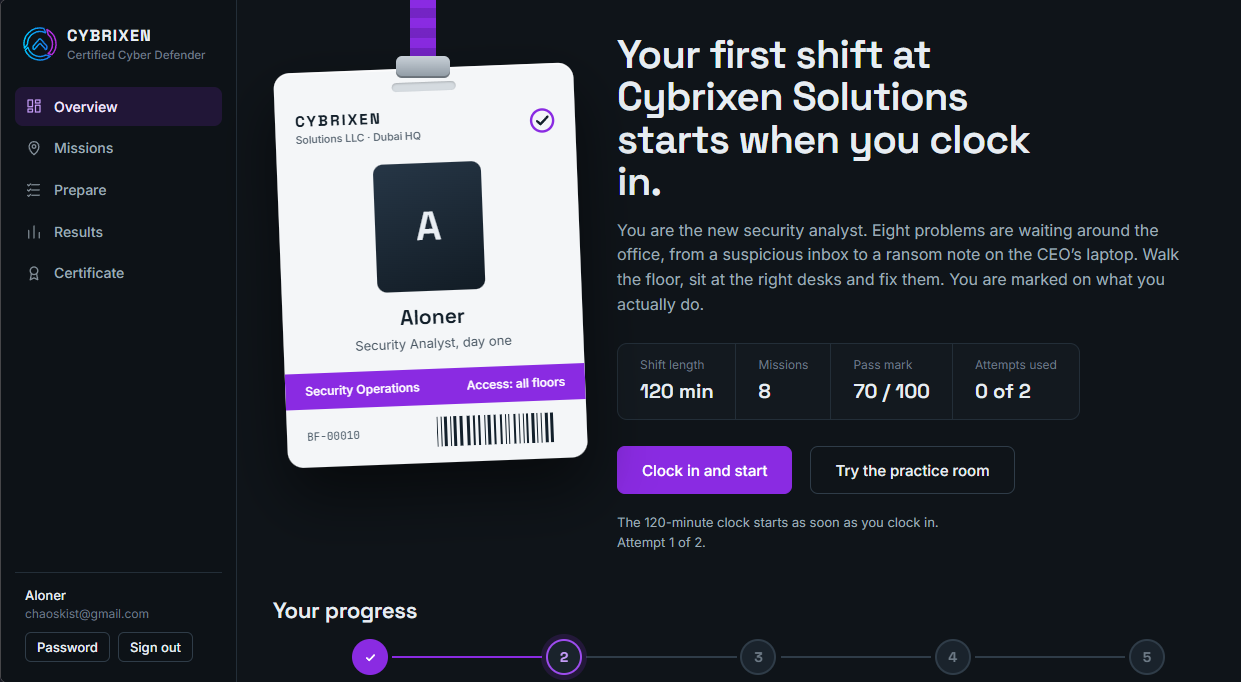
After you buy the exam voucher, 2 emails arrive in your inbox, and one of them has the credentials to sign in to the exam portal. Once signed in, it asks for the name to put on your certificate after you pass. Then you see the exam information along with your access badge to Cybrixen Solutions, where you will work your 120-minute shift.
On this page you can read about all 8 missions in detail: how each one works (including the AI voice-over), its objective, what to deliver, how it is graded, and the layout of each mission area and the whole company. These matter if you want to take the exam. Spend your time here understanding how it works instead of going in blind and figuring things out during the exam. Remember, you only have 2 hours, so you had better spend that time completing all of the missions!
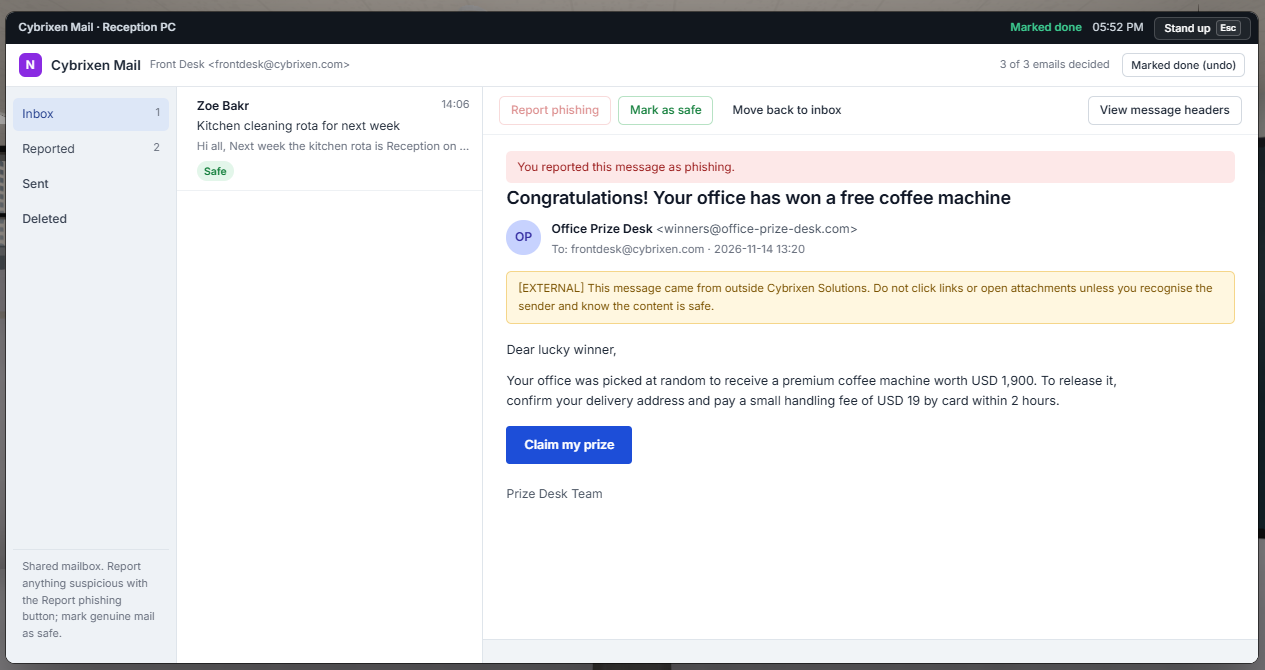
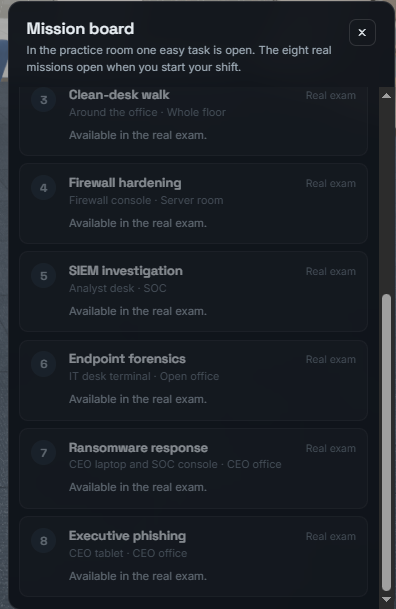
One nice thing CYBRIXEN has done for us is the practice room. You can start it before the exam to learn the layout, how to interact with each object and how the first mission works. All the other missions are locked, so you will have to figure those out in the exam.
Now it's time for the exam itself. Let's go.
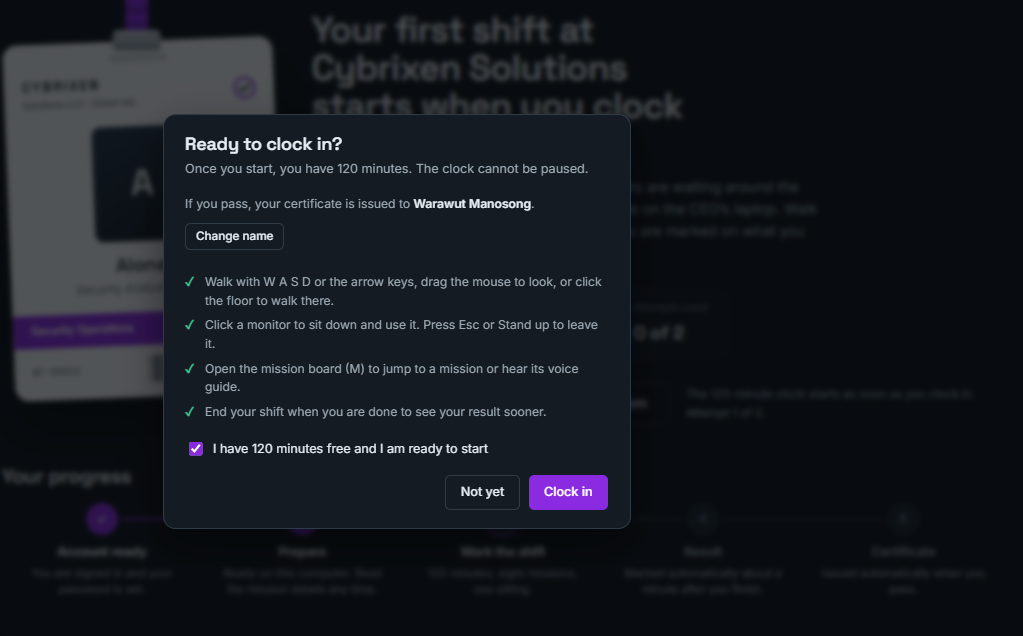
I originally wanted to take the exam on Sunday morning, but my friend Michał started his and passed on Saturday, the day the exam was released, so I started mine as well. When you click "Clock in", it reminds you again to check that your name is correct. Then it shows the basic controls, how to interact with objects and the mission board, plus a little box to tick confirming you have 120 free minutes and are ready to clock in.
Once it started, I went to complete the first mission. Some emails are obvious, but a few are still tricky, and that includes the executive phishing (the last mission) as well.
Then I went on to the second mission, the access review, where there is a policy for us and we have to adjust users' rights and access to match it. I thought I did a good job here, but I missed one policy because the search filter didn't show the group I was looking for. I could blame myself for not looking at each user carefully.
After marking the 2nd mission done, I started my journey on the 3rd one, but after walking around for a while I realized that was not a good choice. So I went to firewall hardening (the 4th mission) while keeping an eye out for anything anomalous.
For the 4th mission, there is a change ticket with requirements for changing the firewall rules, and you can use a packet tracer to confirm a rule was applied correctly before committing it and marking the mission done.
Instead of going to the SIEM investigation (5th mission), I went to endpoint forensics (6th mission), because it was right next to the PC I used for firewall hardening. (Come to think of it, if I had walked into the company normally, I would have done the endpoint before the access review, but never mind.)
Endpoint forensics is not really digital forensics as we would think of it. It is light live forensics on a Linux server stuck at 100% CPU: remove whatever is causing it, verify downloads and fix file permissions. Simple as that.
Now the complex part: ransomware response and executive phishing, which required me to look at the CEO's devices. You complete the last mission here and handle part of the 7th mission; the second half happens in the same room as the 5th mission that I skipped earlier.
After triaging and responding properly in the incident response console, I marked the 7th mission done and completed the 5th next. It was pretty simple, but I got one thing wrong, because of a format issue I think? That left the last one, the 3rd mission, which requires us to look over the whole "floor". The mission board kept telling me how many things there were to discover, so I wandered around the floor again until I noticed the coffee machine. It was there, and I could make some coffee! I somehow made 2 and drank them. I didn't feel any different, but I found the rest of the problems after drinking those 2 cups of virtual coffee, so I guess it had something to do with it XD
I didn't double-check every mission despite having 43 minutes left. Maybe I was too lazy as usual; this habit dies hard, and humans are supposed to be lazy after a working week. ¯\_(ツ)_/¯
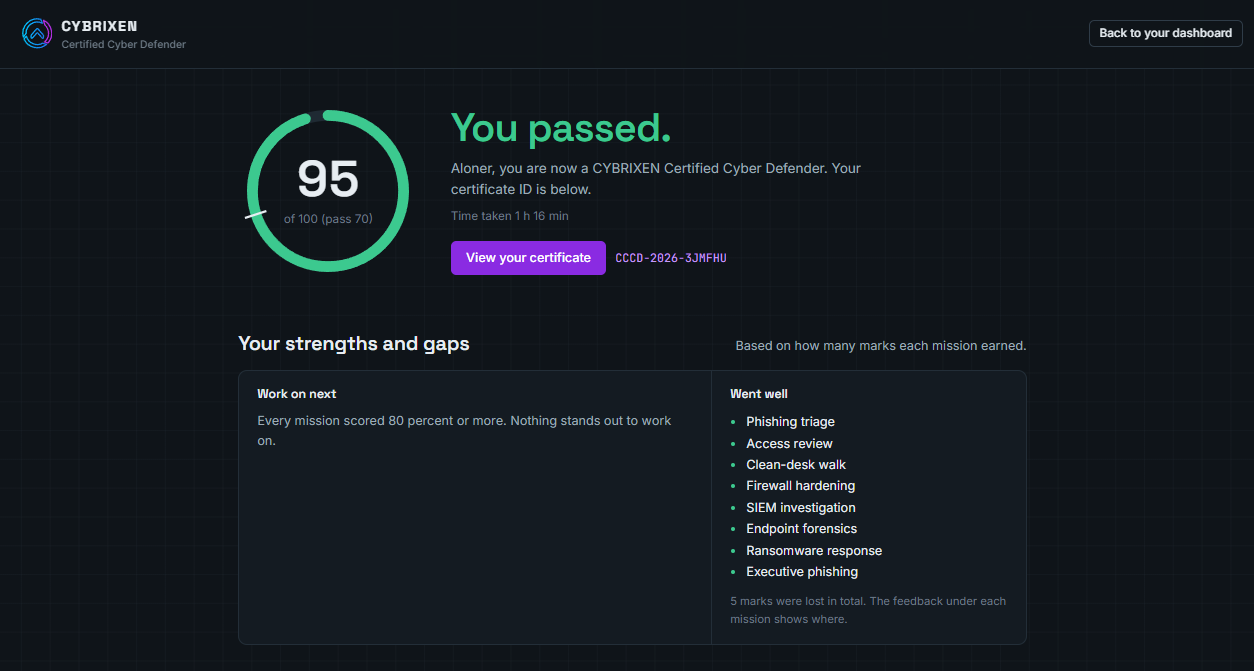
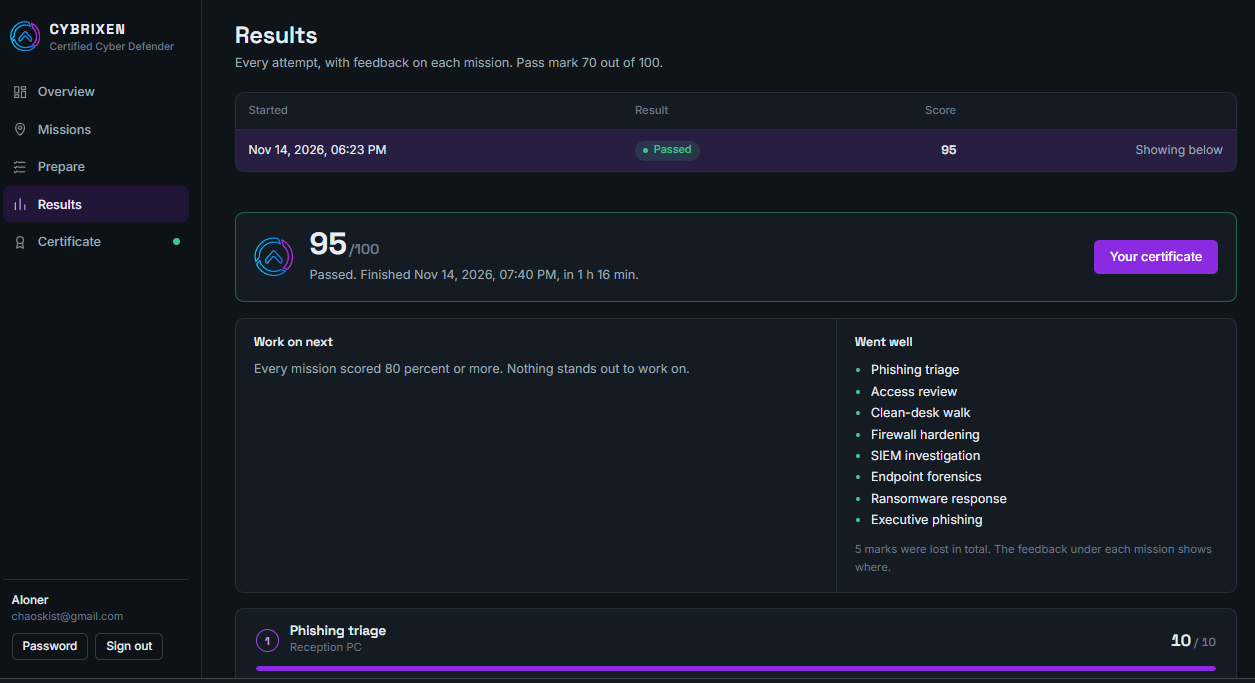
I clocked out, and boom. Unlike my experience with CCSA, where I had to wait for the team to review it, this result was almost instant (around 1 to 2 minutes of automatic checking). I passed with 95/100, and on this page I can see what earned my score and what I missed.
I would say the exam is pretty fun, which is why this blog feels different in the experience part. Compare that with a GIAC exam, where failing means losing 999 USD (before tax) for nothing. This one is really gamified, and free (in my case).
So what is my final thought? Read the next section 😄
CCCD is a fun exam that lets you walk the whole floor of a simulated company and handle 8 different missions. Those missions draw on many areas of cybersecurity: spotting what looks malicious in an event log and what looks phishy in an inbox, plus physical security and a bit of GRC. The GRC side is not full compliance work; it is change management, ticket handling and following policy.
It shows that if you give AI to someone who has an idea and is willing to spend tokens and effort on it, the result can be unique, just like what CYBRIXEN did with all of their exams. If you want something fun, consider taking this exam. I also think CYBRIXEN could build more scenarios with different floors and places, and even market it as a game!
Also, I'm not a fan of the brown colour they put on the CCCD badge, so I hope they change it.
On the job-hunting side, will this certificate do anything for HR? Still no. I don't think the current market needs more certifications. It needs people who can use AI to do their jobs better than everyone else (like a 10x engineer, but a 100x SOC analyst or DFIR analyst), or seasoned professionals who aren't replaceable, like folks who have actually been through trials and know how to handle them properly, and no certificate can prove that. So take this certification for fun, but don't expect too much from it for promotions and job opportunities.